How Can a Mobile App Development Company Improve App Security?
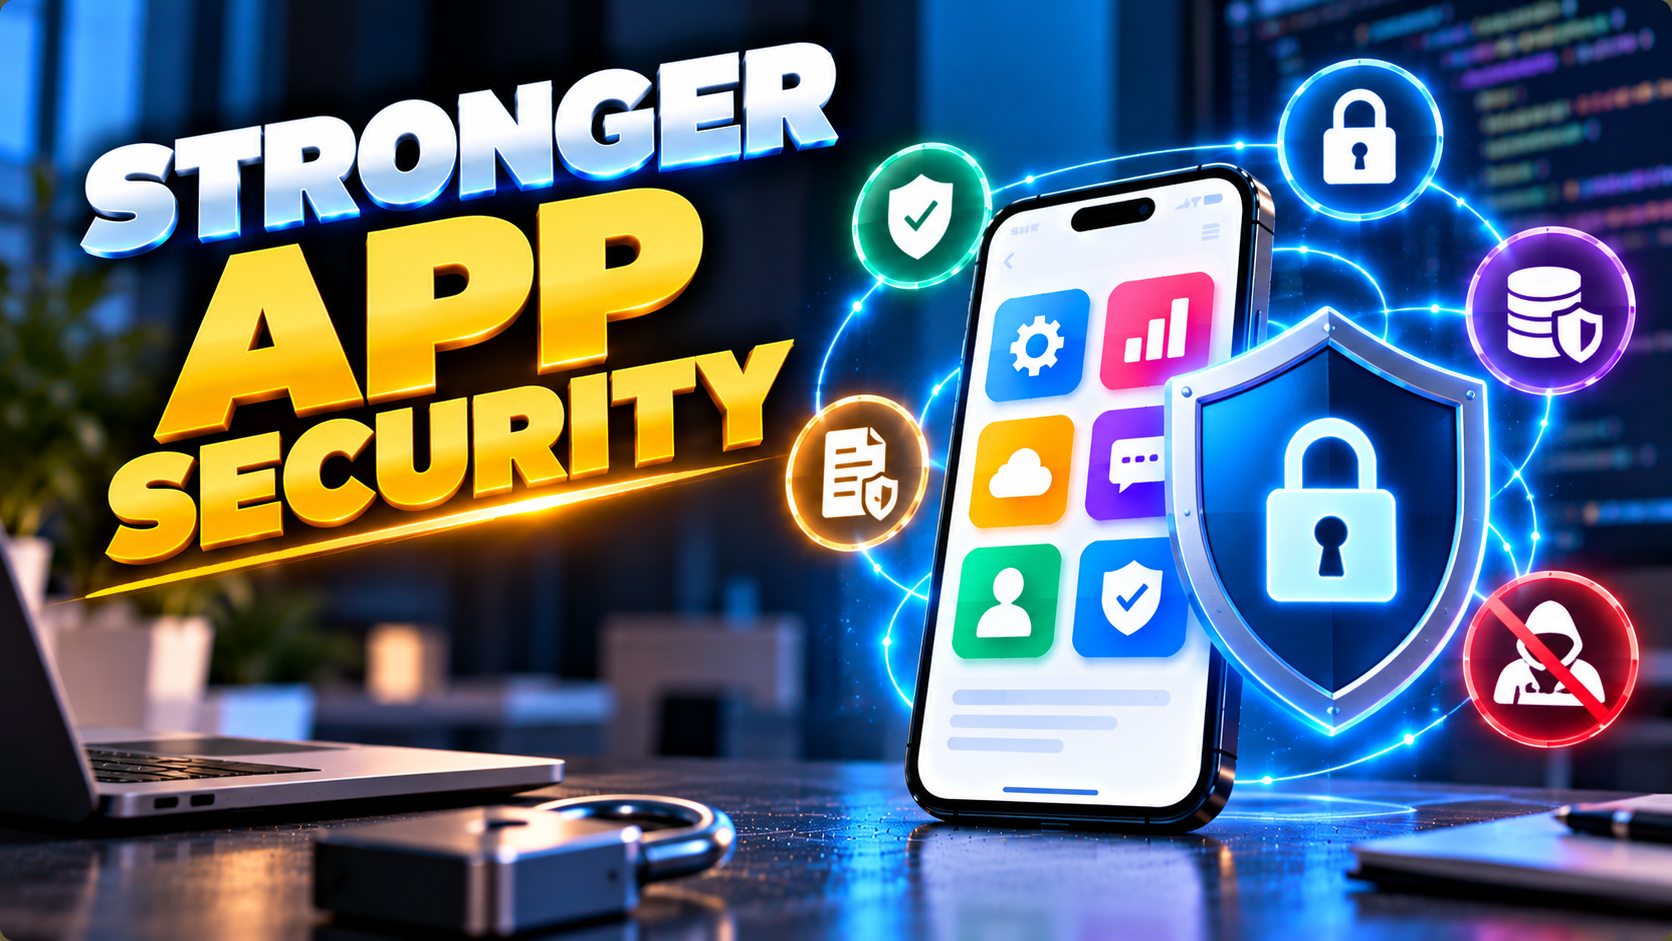
Mobile app development company services play an important role in protecting business applications against data breaches, unauthorized access, and evolving cyber threats. As mobile apps handle sensitive customer information, financial transactions, and business operations, security must be considered from the earliest planning stages rather than added after development. A secure app protects users, strengthens brand credibility, and helps businesses maintain reliable digital services.
However, improving app security requires more than installing protective software. It involves thoughtful architecture, secure coding practices, appropriate access controls, continuous testing, and regular updates. Understanding these measures helps businesses choose the right development partner and make informed decisions about their application security.
Why Is Mobile App Security Important for Businesses?
Mobile applications frequently process personal information, login credentials, payment details, location data, and confidential business records. If attackers exploit weaknesses in an application, the consequences may include financial losses, customer complaints, operational disruption, and reputational damage.
Security is particularly important for applications used in e-commerce, healthcare, banking, logistics, and enterprise management. A vulnerability in any of these environments can expose information that users and organizations expect to remain confidential.
A secure mobile application protects not only its data but also the trust customers place in the business.
Development teams should therefore identify potential risks before launch and establish a security strategy that continues throughout the application’s lifecycle.
How Does a Mobile App Development Company Strengthen App Security?
A reliable development team combines several security measures to reduce vulnerabilities and protect application data.
1. Implementing Strong Authentication and Authorization
Authentication verifies a user’s identity, while authorization determines what that user can access. Both are essential for preventing unauthorized activity.
Development teams can strengthen these controls by implementing:
- Multi-factor authentication for sensitive accounts and operations.
- Secure password storage using appropriate password-hashing algorithms.
- Role-based access controls for different user categories.
- Session expiration and secure logout mechanisms.
- Protection against repeated login attempts and credential abuse.
For example, an employee management app should not allow every employee to access payroll records or administrative settings. Access permissions must match each user’s responsibilities.
2. Encrypting Sensitive Information
Encryption helps prevent unauthorized parties from reading protected information, even if they gain access to stored data or intercepted communications.
A development team should consider encryption at two important levels:
Data in transit: Use properly configured HTTPS and modern TLS to protect communication between the mobile app and its servers.
Data at rest: Encrypt sensitive information stored on devices, servers, or databases when appropriate.
Applications should also avoid storing confidential information unnecessarily. Where sensitive credentials or tokens must be retained, developers should use platform-provided secure storage mechanisms, such as the iOS Keychain or Android Keystore, according to the application’s requirements.
3. Following Secure Coding Practices
Security weaknesses can originate directly in the application code. Improper input validation, insecure authentication logic, exposed secrets, and unsafe data handling can create opportunities for attackers.
Secure development practices help reduce these risks.
Teams should validate user inputs, handle errors without exposing confidential details, protect API endpoints, and avoid embedding private keys or secret credentials in application code. They should also review third-party libraries and dependencies for known vulnerabilities.
Code reviews and automated security checks can identify potential issues before they reach production.
4. Protecting APIs and Backend Services
Mobile applications commonly communicate with backend systems through APIs. Even when the app interface appears secure, poorly protected APIs can expose sensitive business data.
A mobile app development company should implement appropriate API security controls, including:
- Authentication and permission checks on the server.
- Input validation and safe error handling.
- Rate limiting to reduce abuse and automated attacks.
- Secure token management and expiration.
- Monitoring for suspicious requests and unusual access patterns.
One important principle is that security decisions must be enforced on the server, not only within the mobile application. Attackers may modify or bypass client-side controls, so backend systems must independently verify every sensitive request.
What Role Do Regular Updates Play in App Security?
Launching a secure application does not guarantee that it will remain secure indefinitely. New vulnerabilities may emerge in operating systems, development frameworks, libraries, and backend infrastructure.
Regular maintenance helps businesses respond to these changes.
A practical security maintenance plan includes:
- Updating vulnerable dependencies and development frameworks.
- Applying security patches to backend services and infrastructure.
- Reviewing authentication and access-control policies.
- Monitoring application logs for suspicious activity.
- Testing critical workflows after security-related changes.
- Establishing a process for reporting and responding to vulnerabilities.
Businesses should also plan how urgent security fixes will reach users. A well-maintained application can respond more effectively when a newly discovered vulnerability requires immediate attention.
How Can Businesses Choose a Security-Focused Development Partner?
Choosing a development partner involves evaluating its technical capabilities and its approach to managing risk.
Before starting a project, businesses should ask how the team handles encryption, authentication, API protection, vulnerability testing, third-party dependencies, and ongoing maintenance.
It is also useful to understand who is responsible for security reviews, how critical vulnerabilities are reported, and whether security requirements are documented in the project scope.
Look for a team that explains security decisions clearly instead of promising that an application will be completely immune to attacks. No development process can eliminate every risk, but a structured security approach can significantly reduce exposure and improve resilience.
Businesses should also consider whether the development partner can support future requirements, such as additional user roles, payment integrations, enterprise systems, or increased data-processing demands, without compromising existing security controls.
Conclusion
Improving mobile app security requires a combination of secure architecture, strong authentication, encryption, protected APIs, thorough testing, and continuous maintenance. Businesses that address these areas early can reduce avoidable vulnerabilities, protect sensitive information, and provide users with a more dependable digital experience.
The right development partner should treat security as an ongoing responsibility rather than a one-time technical task. From initial planning to post-launch updates, every stage should support the application’s security objectives and business requirements.
For secure and scalable apps, explore our mobile app development solutions to support your business growth.
Frequently Asked Questions
1. How does a mobile app development company improve app security?
It improves security through secure coding, encryption, authentication, API protection, vulnerability testing, and regular software updates. The exact measures depend on the application’s features and risk profile.
2. What are the most common mobile app security risks?
Common risks include weak authentication, insecure data storage, exposed API endpoints, improper access controls, vulnerable third-party libraries, and insufficient input validation.
3. Is encryption enough to secure a mobile application?
No. Encryption protects data in specific situations, but an application also needs secure authentication, server-side authorization, safe coding practices, security testing, and ongoing maintenance.
4. When should mobile app security testing begin?
Security testing should begin during planning and design, continue throughout development, and take place before release. Regular checks are also necessary after launch as the application and its dependencies change.
5. How often should a mobile app undergo security reviews?
Security reviews should be continuous for important changes, with periodic assessments based on the app’s risk level. Critical vulnerabilities should be investigated and addressed promptly rather than waiting for a scheduled review.
Location

Leave a Comment